Skip to content
No results
  • Home
  • About Us
  • Blog
  • Service
    • Decision Support
    • Product Auditing
    • Product Selection
    • Stack Optimization
  • Contact Us
MSSP Security Consulting | Product Strategy & Auditing Experts
  • Home
  • About Us
  • Blog
  • Service
    • Decision Support
    • Product Auditing
    • Product Selection
    • Stack Optimization
  • Contact Us
MSSP Security Consulting | Product Strategy & Auditing Experts
  • Comparing SIEM Platforms MSSP Uses, qradar managed siem review in Fullerton, Technology and Platforms Utilized

QRadar Managed SIEM Review in Fullerton: Honest Take
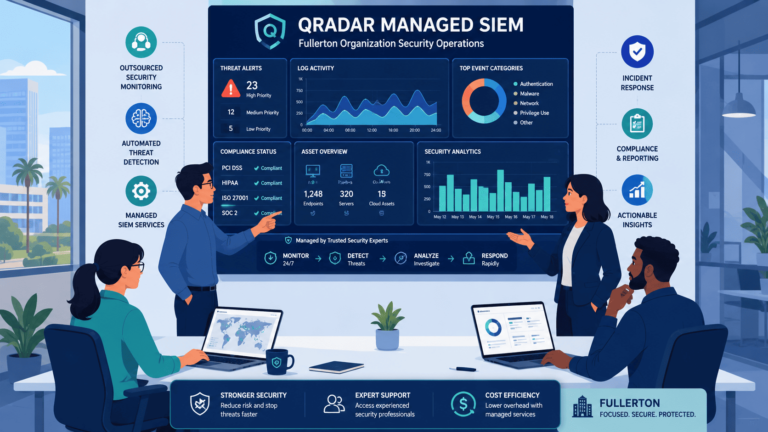
Security team monitors live dashboard during Qradar managed Siem review in Fullerton showing compliance and threat alert status.

A managed QRadar SIEM is a solid option for Fullerton companies that want enterprise-level threat detection without running their own security team. IBM’s data shows customers who properly set up QRadar spend much less time investigating incidents. The real value,…
  • Richard K. Stephens
  • June 26, 2026
  • Comparing SIEM Platforms MSSP Uses, Technology and Platforms Utilized

Choosing SIEM for Security Outsourcing That Fits Your Needs

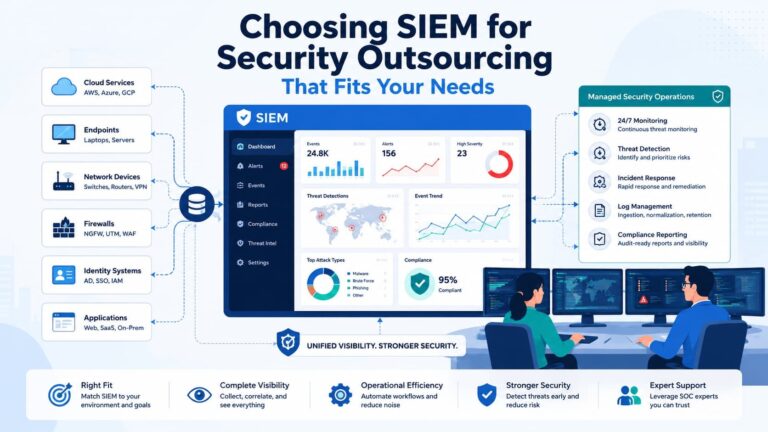
An IT team choosing SIEM for security outsourcing with unified visibility and managed SOC operations.

Choosing a SIEM for security outsourcing starts with finding a platform that fits your operational needs, not the most recognizable name in the market. At MSSP Security, we’ve seen organizations achieve better outcomes when their SIEM, detection workflows, and service…

  • Richard K. Stephens
  • June 26, 2026
  • Comparing SIEM Platforms MSSP Uses

Comparing SIEM Platforms MSSP Uses for Better Threat Detection 

Dashboard view comparing SIEM platforms MSSP uses to monitor client networks.

Choosing the right SIEM platform is one of the most important decisions for an MSSP Security provider. The platform affects threat detection speed, operational efficiency, reporting, and long-term costs while supporting multiple clients.  Comparing SIEM platforms MSSP uses also helps…

  • Richard K. Stephens
  • June 24, 2026
  • Newsroom

Secure Cloud Migration and the $80B Cloud Shift 

Portable server cases staged in urban facility representing physical infrastructure for secure cloud migration

We’ve been watching the Polytechnique decision unfold, and honestly? It’s bigger than most people realize. That French university didn’t just suspend Microsoft 365 over the US Cloud Act, they exposed a fundamental crack in how we think about “secure cloud…

  • Richard K. Stephens
  • June 24, 2026
  • Secure Cloud Migration

Secure Cloud Migration and the Compliance Gap

Server health dashboard and compliance audit binder supporting secure cloud migration planning

The Polytechnique decision is a warning shot. It exposed the legal fault line where the US Cloud Act collides with GDPR, making traditional cloud contracts a liability minefield for European institutions. This isn’t a theoretical debate anymore, it’s an operational…

  • Richard K. Stephens
  • June 24, 2026
  • Technology and Platforms Utilized

Technology and Platforms Utilized: The Security Stack Behind Modern MSSP Protection 

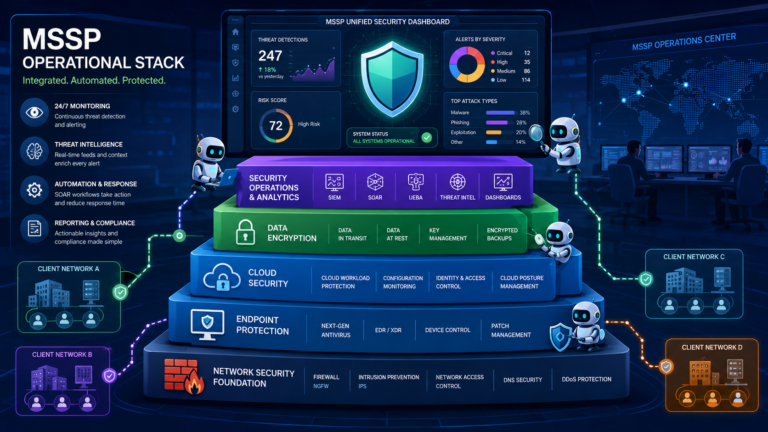
A clean vector illustration showing a leader using a magnifying glass to evaluate key technology and platforms utilized by an MSSP. 

Modern cybersecurity depends on more than individual security tools. The technology and platforms utilized by an MSSP determine how effectively threats are detected, investigated, and contained. At MSSP Security, we have found that strong protection starts with visibility.  That is…

  • Richard K. Stephens
  • June 23, 2026
  • Comparing SIEM Platforms MSSP Uses, Technology and Platforms Utilized

Splunk vs Sentinel MSSP Comparison: Which SIEM Fits Modern MSSPs?

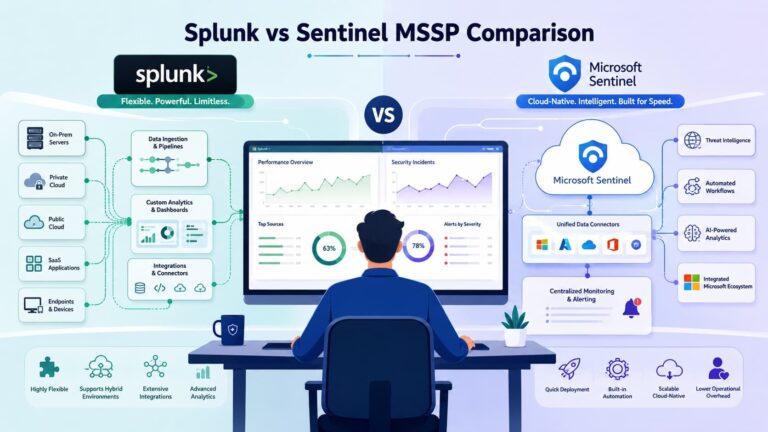
Side-by-side platform overview for a splunk vs sentinel mssp comparison showing hybrid and cloud-native capabilities.

For MSSPs, the choice between Splunk and Microsoft Sentinel is less about features and more about operational fit. At MSSP Security, we see this decision shaped primarily by architecture, onboarding complexity, and customer environment. Industry data shows Sentinel can slash…

  • Richard K. Stephens
  • June 23, 2026
  • automating threat intel response, Operations & Delivery Mechanisms, Threat Intelligence Integration Actioning

Automating Threat Intel Response in Real Time

SOC analyst overwhelmed by alerts contrasted with SOAR robot automating threat intel response in real time

Automating threat intelligence response helps security teams turn threat data into action faster. Instead of handling every task manually, teams can automate intelligence collection, enrichment, prioritization, and response across the workflow. According to IBM’s Cost of a Data Breach research,…

  • Richard K. Stephens
  • June 23, 2026
  • Threat Intelligence Integration Actioning, operationalizing threat intelligence soc, Operations & Delivery Mechanisms

Operationalizing Threat Intelligence SOC Success

SOC analyst monitoring dashboards, operationalizing threat intelligence SOC workflows for actionable cybersecurity outcomes.

Meta description: See how operationalizing threat intelligence SOC programs turn CTI into daily detection, triage, and response outcomes. Threat intelligence creates value only when it drives action. Industry research shows that organizations get better results when intelligence is built into…

  • Richard K. Stephens
  • June 23, 2026
  • Threat Intelligence Integration Actioning

Communicating Threat Intel Insights Client for Clear Decisions 

Communicating Threat Intel Insights Client presented to executives using a cyber risk dashboard in a boardroom

Communicating threat intel insights to clients works when technical findings are translated into risk, business impact, and clear next steps. Many organizations receive large volumes of indicators but still struggle to decide what actions to take. Security leaders need reporting…

  • Richard K. Stephens
  • June 22, 2026
Prev
1 … 12 13 14 15 16 17 18 … 58
Next
MSSP Security Consulting | Product Strategy & Auditing Experts

MSSP Security provides vendor-neutral product strategy, independent auditing, and security stack optimization purpose-built for Managed Security Service Providers. We help MSSPs cut through vendor noise — evaluating, selecting, and maximizing the right cybersecurity tools based solely on your operational needs and client outcomes. No hidden partnerships. No affiliate bias. Just clear, objective guidance that drives measurable results across your entire security practice.

Request a Consultation →
  • Service
  • Decision Support
  • Product Auditing
  • Product Selection
  • Stack Optimization

Copyright © 2026 MSSP Security. All Rights Reserved.