Skip to content
No results
  • Home
  • About Us
  • Blog
  • Service
    • Decision Support
    • Product Auditing
    • Product Selection
    • Stack Optimization
  • Contact Us
MSSP Security Consulting | Product Strategy & Auditing Experts
  • Home
  • About Us
  • Blog
  • Service
    • Decision Support
    • Product Auditing
    • Product Selection
    • Stack Optimization
  • Contact Us
MSSP Security Consulting | Product Strategy & Auditing Experts
  • incident responder required skills

Incident Responder Required Skills: Essential Abilities for Cybersecurity Response Teams

Essential incident responder required skills for cybersecurity teams featuring threat analysis and tool proficiency. 

Cybersecurity incidents can happen at any time, making skilled incident responders essential for modern security operations. Incident responders investigate attacks, contain threats, and help organizations recover from security breaches quickly and efficiently.  The incident responder required skills combine technical expertise,…

  • Richard K. Stephens
  • May 20, 2026
  • security engineer soc responsibilities

Security Engineer SOC Responsibilities: Supporting Modern Security Operations

Security engineer SOC responsibilities shown via professional at a command center managing cloud and infrastructure.

Security Operations Centers rely on strong technical teams to maintain visibility, improve detection, and protect business infrastructure from cyber threats. Security engineer SOC responsibilities focus on building, managing, and improving the technologies that support security operations.  These professionals help maintain…

  • Richard K. Stephens
  • May 19, 2026
  • threat hunter role description

Threat Hunter Role Description: Responsibilities, Skills, and Career Path

A threat hunter role description illustration showing an expert analyzing a digital shield with skill icons. 

Cyber threats continue evolving faster than traditional security defenses. Organizations now rely on proactive security specialists who search for hidden threats before damage occurs. A strong threat hunter role description includes threat detection, behavioral analysis, incident investigation, and continuous monitoring…

  • Richard K. Stephens
  • May 18, 2026
  • Skills Needed Security Analyst

Skills Needed Security Analyst: Core Abilities for Modern Cyber Defense

Security analyst at a desk with three screens showing the core skills needed security analyst for cyber defense. 

Cybersecurity teams depend on skilled analysts to monitor threats, investigate incidents, and protect business systems from attacks. The skills needed security analyst professionals develop combine technical knowledge, communication, and problem-solving.  These abilities help security teams respond faster and improve operational…

  • Richard K. Stephens
  • May 17, 2026
  • soc analyst tier 1 2 3 responsibilities

SOC Analyst Tier 1 2 3 Responsibilities: How We Structure Real Cyber Defense Work

Circular flowchart mapping SOC analyst tier 1 2 3 responsibilities in a collaborative MSSP environment. 

In real SOC environments, cybersecurity work is never handled as a single flat process. In our day-to-day operations at MSSP Security, we rely on a structured layered model where soc analyst Tier 1 2 3 responsibilities work together as one…

  • Richard K. Stephens
  • May 16, 2026
  • Roles Within Security Operations Center

Roles Within Security Operations Center (SOC): How Cyber Defense Teams Work Together

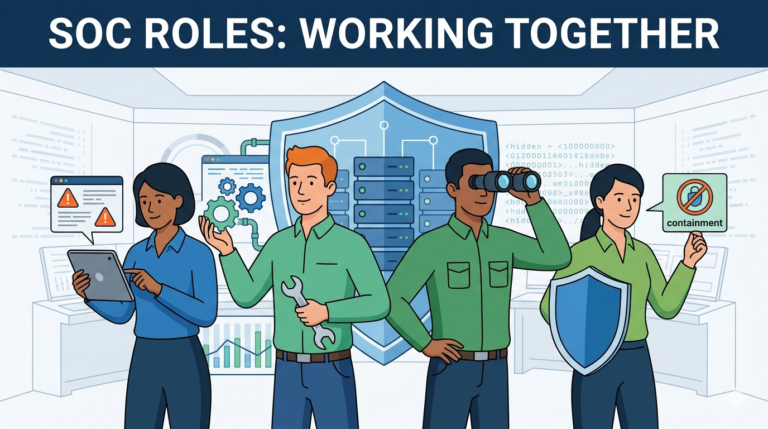
A team of four professionals representing core roles within security operations center, standing in front of a digital shield. 

A Security Operations Center (SOC) is not a single job, it is a coordinated system of roles working together to detect, analyze, and respond to cyber threats. Roles within Security Operations Center define how efficiently security incidents are handled from…

  • Richard K. Stephens
  • May 15, 2026
  • soc analyst daily activities

SOC Analyst Daily Activities: Inside Modern Security Operations Centers

Professional workstation showing SOC analyst daily activities like real-time monitoring and incident ticketing. 

SOC analyst daily activities focus on monitoring security systems, investigating alerts, and responding to potential threats. In MSSP Security operations, we handle multiple client environments, so prioritization and accuracy are very important. Each day involves reviewing logs, checking alerts, and…

  • Richard K. Stephens
  • May 14, 2026
  • Security Analyst Roles Expertise

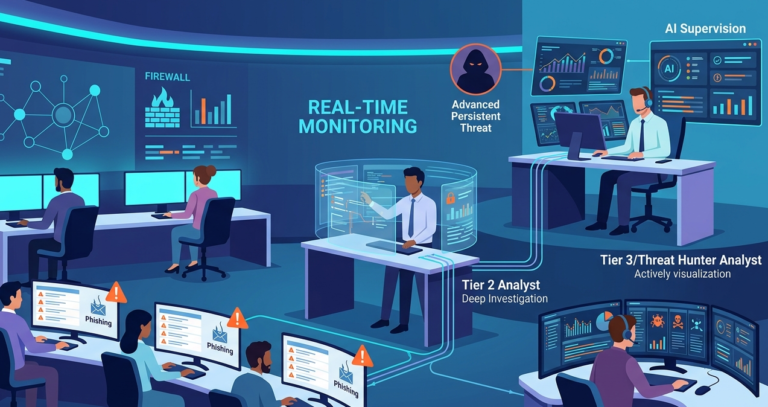
Security Analyst Roles Expertise: Inside Modern SOC Operations and Real-World Cyber Defense

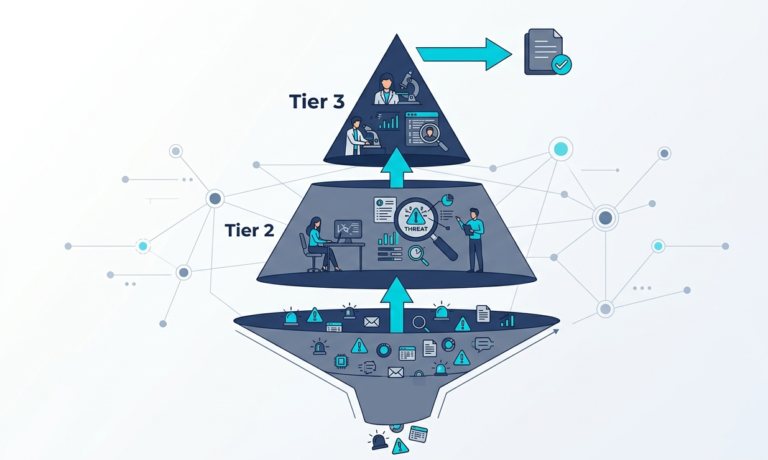
Modern SOC tiered hierarchy showing Tier 1, 2, and 3 Security Analyst Roles Expertise in a digital control room. 

Security Analyst Roles Expertise is best understood through how Security Operations Centers (SOC) function in real time. In MSSP Security environments, we don’t just observe threats, we continuously monitor, analyze, and respond to them across multiple clients and systems.  Every…

  • Richard K. Stephens
  • May 13, 2026
  • measuring remediation success metrics

Measuring Remediation Success Metrics: Turning Security Actions into Measurable Results

Analyst pointing to a 100% success dashboard, measuring remediation success metrics in a modern vector office. 

Fixing a security issue is only part of the job, proving that the fix works is what really matters. From our experience, many teams execute remediation but fail to measure its effectiveness. This creates gaps in visibility and weakens automated…

  • Richard K. Stephens
  • May 12, 2026
  • post incident remediation activities

Post Incident Remediation Activities: Strengthening Security After an Incident

Team and robot performing post incident remediation activities by mending a digital security shield. 

An incident doesn’t end when the threat is removed, it ends when the root cause is fixed. From our experience, many organizations focus only on containment, ignoring what comes next. Post incident remediation activities are critical to ensure the same…

  • Richard K. Stephens
  • May 11, 2026
Prev
1 … 11 12 13 14 15 16 17 … 53
Next
MSSP Security Consulting | Product Strategy & Auditing Experts

MSSP Security provides vendor-neutral product strategy, independent auditing, and security stack optimization purpose-built for Managed Security Service Providers. We help MSSPs cut through vendor noise — evaluating, selecting, and maximizing the right cybersecurity tools based solely on your operational needs and client outcomes. No hidden partnerships. No affiliate bias. Just clear, objective guidance that drives measurable results across your entire security practice.

Request a Consultation →
  • Service
  • Decision Support
  • Product Auditing
  • Product Selection
  • Stack Optimization

Copyright © 2026 MSSP Security. All Rights Reserved.