

A gap analysis presentation should show management where performance falls short, why it matters, and which decisions are needed. MSSP Security ties findings to business priorities, risks, and practical next steps. This guide covers executive briefings, supporting evidence, and remediation approval. Keep reading to learn how to present findings clearly.
Quick Insights: What Makes a Gap Analysis Presentation Effective?
When presenting gap analysis findings to management, focus on three points:
- Lead with impact: Explain how each gap affects objectives, operations, or risk.
- Set priorities with evidence: Compare current and target performance, then rank gaps.
- Clarify decisions: Identify specific actions, owners, deadlines, resources, and required approvals for management.
How Should You Structure a Gap Analysis Presentation for Executives?
A gap analysis presentation for executives should explain what an assessment found, how those findings affect the business, and which decisions management needs to make. For MSSPs reviewing new products, the presentation should also show whether a vendor’s solution meets technical, security, and operational requirements.
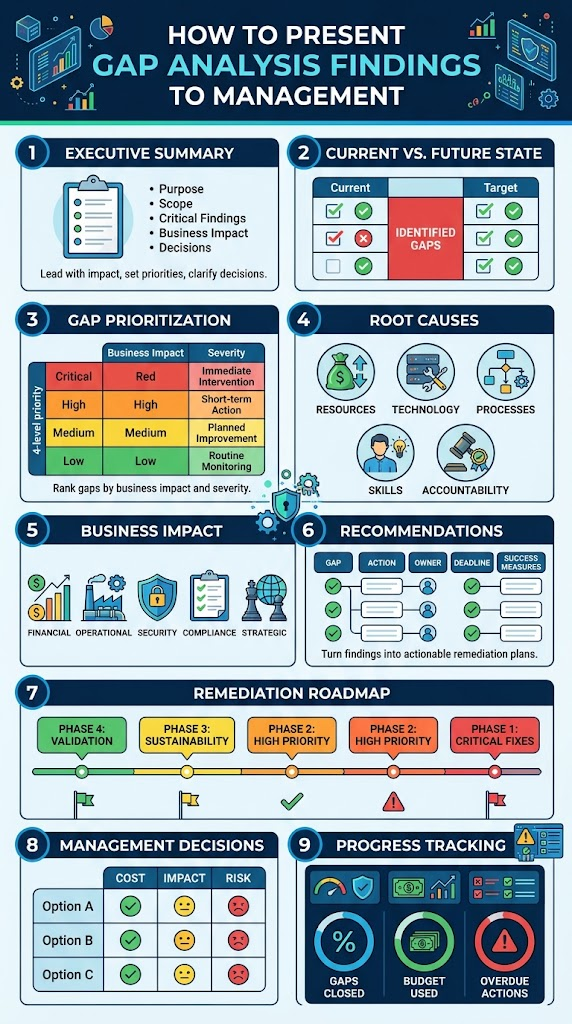
We organize the findings around eight areas:
- Executive summary
- Assessment scope and objectives
- Current versus desired future state
- Critical findings and product gaps
- Business impact and associated risks
- Prioritized recommendations
- Remediation roadmap
- Management decisions and next steps
This order takes management from the reason for the assessment to the decisions that follow. It also keeps technical details from overshadowing the issues that need approval. A well-organized MSSP gap analysis report can support this presentation by documenting assessment findings, identifying product deficiencies, and connecting each issue to the MSSP’s business and operational requirements.
What Should an Executive Gap Analysis Presentation Include?
Each section should answer a question management is likely to ask.
For an MSSP evaluating a new security product, that means explaining whether the product meets the organization’s requirements. The assessment may cover access management, incident response, monitoring, integration, reporting, and compliance. If a product falls short in one of these areas, the presentation should identify the requirement and show what the assessment found.
The National Institute of Standards and Technology (NIST) Cybersecurity Framework 2.0, published in 2024, offers a useful structure for discussing cybersecurity outcomes. Its six functions are Govern, Identify, Protect, Detect, Respond, and Recover. We can use these categories to organize findings so technical teams and executives have a shared reference point.
How Long Should an Executive Presentation Be?
Keep the main presentation focused on findings that affect a decision. Around 10 to 15 slides can work for many assessments, although the right length depends on the number of products, requirements, and issues under review. This is a suggested format, not a fixed standard.
Detailed test results, interview notes, product specifications, and assessment methods can go into an appendix. Management gets the main findings first, while technical reviewers can still examine the supporting material.
Leave time for questions, too. Executives may need to discuss cost, vendor dependencies, security concerns, or the effort involved in adopting a product. Those questions should be part of the presentation plan, not an afterthought.
What Should an Executive Summary for Gap Analysis Communicate?
An executive summary should identify the main gaps, explain their business consequences, and state what management needs to decide. It should give readers enough information to understand the assessment without asking them to work through the full report.
For MSSPs considering a new product, we connect each major finding to a business or service requirement. A product may have the features listed in its sales material but still fall short of an MSSP’s needs for integration, control, reporting, or day-to-day operation. The summary should make that distinction clear.
What Are the Essential Components?
A useful executive summary covers six areas:
- Assessment purpose: Why was the product or process reviewed?
- Assessment scope: Which products, systems, teams, processes, or controls were included?
- Overall results: How well does the product or organization meet the stated requirements?
- Critical findings: Which deficiencies need management attention?
- Business implications: What are the possible financial, operational, or security consequences?
- Recommended actions: What should happen next, and which decisions require approval?
For example, a product review may find that access reviews are not sufficiently supported by the product’s available controls or reporting. The summary should identify the affected requirements, point to the evidence, and explain whether the gap calls for a configuration change, an additional process, or a different product.
How Can You Write a Decision-Oriented Summary?
A comparison table helps management follow the assessment without getting lost in technical detail.
| Component | Key question |
| Current state | What can the product or process do now? |
| Desired state | What does the MSSP require? |
| Critical gaps | Which requirements are not being met? |
| Business impact | Why does each gap matter? |
| Recommended action | What should happen next? |
| Management decision | What approval or direction is needed? |
Keep technical terminology out of the executive summary unless it’s genuinely needed to clarify a finding. A short description of the requirement, the evidence, and the consequence gives management far more clarity than a lengthy breakdown of the assessment method.
How Do You Compare the Current State Against the Desired Future State?
A current-versus-future-state comparison shows where an existing product, process, or capability falls short of the requirements. It gives management a reference point for judging whether a proposed product is suitable and what would need to change before adoption.
Before making recommendations, define two things: the current condition and the required condition. Without both, a gap rating has little meaning.
What Should a Current vs. Future State Assessment Include?
A useful comparison covers five areas:
- Existing product capabilities or processes.
- Required performance standards.
- Identified deficiencies.
- Expected improvements.
- Evidence supporting each finding.
Consider an MSSP reviewing a product’s access management capabilities. The current state may show that access reviews rely on manual checks and inconsistent records. The required state may call for scheduled reviews, assigned approval responsibilities, and records that can be examined during an audit.
The difference between those conditions is the gap. The assessment should show whether the product can meet the requirement through its existing features, needs additional configuration, or depends on a separate process.
How Can You Visualize the Differences?
A comparison table makes it easier to see where a product or process meets the requirement and where it does not.
| Assessment area | Current state | Desired state | Identified gap |
| Processes | Manual procedures | Documented workflows | Process deficiency |
| Skills | Limited technical training | Defined competency requirements | Skills shortage |
| Security | Inconsistent access reviews | Scheduled access reviews | Control deficiency |
| Compliance | Incomplete documentation | Complete audit records | Compliance gap |
| Monitoring | Reactive reporting | Continuous monitoring | Visibility deficiency |
For cybersecurity assessments, we can use the six NIST CSF 2.0 functions to group findings across governance, identification, protection, detection, response, and recovery.
The target state must also fit the MSSP’s actual needs. A requirement may come from a customer commitment, regulatory obligation, internal security policy, or service delivery model. Setting a target that ignores available staff, budget, or technical dependencies can leave the business with a remediation plan it cannot carry out.
Which Gap Analysis Findings Should Management Prioritize?
Alt text: Cybersecurity team developing a remediation plan to address identified gap analysis findings.
Management should rank gaps by business impact, severity, risk exposure, urgency, and the effort needed to address them.
Management should rank gaps by business impact, severity, risk exposure, urgency, and the effort needed to address them. According to DeepStrike, “over 74% of cybersecurity breaches involve human error,” making organizational gap analysis and staff training critical priorities for management.
A vulnerability assessment gap analysis can also help identify security weaknesses, evaluate their potential impact, and determine which vulnerabilities require immediate attention. A product review may uncover several shortcomings, but not all of them carry the same consequences.
How Should You Rate Gap Severity?
We assess findings against five considerations:
- Potential disruption to service delivery.
- Financial consequences.
- Regulatory or contractual exposure.
- Security weaknesses.
- Conflict with business or service requirements.
For cybersecurity reviews, the NIST Cybersecurity Framework offers a structure for considering risk management outcomes. Its 2024 CSF 2.0 release added the Govern function, which gives management a clear place to consider oversight and accountability alongside technical security activities.
How Can You Build a Gap Prioritization Matrix?
A four-level matrix gives teams a common way to rate findings. The criteria behind each rating should be documented so different reviewers apply them consistently.
| Priority | Characteristics | Management response |
| Critical | Significant business exposure | Immediate intervention |
| High | Major operational impact | Short-term remediation |
| Medium | Manageable performance deficiency | Planned improvement |
| Low | Limited immediate consequences | Routine monitoring |
An unresolved vulnerability in a business-critical system may receive a critical rating. An outdated internal procedure with limited operational consequences may fall into the medium or low category.
A heat map can show how these ratings are distributed across products, departments, or assessment areas. Use the same definitions throughout the review. Otherwise, a “high” rating from one team may mean something different to another.
Dependencies also matter. A medium-rated gap may need attention before a critical remediation task if resolving it is a prerequisite for that work. The priority should reflect the full implementation plan, not only the rating in isolation.
How Can You Explain the Root Causes Behind Identified Gaps?
Credit: SANS Institute
Root cause analysis explains why a product or process fails to meet a requirement. Without that explanation, management may approve a fix that addresses the visible problem but leaves the underlying issue in place.
A recurring access control problem, for example, may result from unclear ownership, a limitation in the product, or a gap in the organization’s review process. Each cause calls for a different response. Buying another tool will not resolve an accountability problem.
What Causes Organizational Performance Gaps?
Common causes include:
- Insufficient resources or funding.
- Outdated or unsuitable technology.
- Ineffective processes.
- Skills or knowledge deficiencies.
- Unclear accountability.
- Inadequate policies or controls.
The GAO Green Book offers a useful reference when examining internal control weaknesses. Its five components include risk assessment, information and communication, and monitoring. These areas help teams consider why deficiencies develop and why they may remain unresolved. The 2025 revision, effective beginning in fiscal year 2026, also addresses risk documentation and information security considerations.
How Should You Present Root Cause Evidence?
For each major finding, document four things:
- Observed problem: What specific requirement is not being met?
- Supporting evidence: Which records, interviews, tests, or assessment results confirm the finding?
- Underlying cause: Is the issue related to the product, configuration, process, resources, or control ownership?
- Potential consequence: What could happen if the gap remains open?
For example, an MSSP may find that a security product does not produce complete incident records. Further review may show that the product lacks a required reporting function, while the team’s procedures also leave reporting responsibilities unclear.
Those are two separate issues. The product limitation may require a different solution or an additional integration. The process issue calls for clearer reporting procedures and assigned ownership. Keeping the causes separate helps management choose a response that addresses both.
How Do You Demonstrate the Business Impact of Identified Gaps?
Explain the financial, operational, security, compliance, or strategic consequences of each significant gap. Management needs to understand what a product deficiency means for the business, not only which technical requirement it fails to meet.
We connect assessment findings to the services an MSSP provides and the commitments it makes to customers. A weakness in monitoring, for example, may affect how the team detects and investigates suspicious activity. That operational consequence gives the finding context.
Which Business Impacts Should You Quantify?
Consider five categories:
- Financial: Additional operating costs, potential losses, or unexpected remediation expenses.
- Operational: Reduced productivity, process delays, or service interruptions.
- Security: Greater exposure to unauthorized access, data loss, or security incidents.
- Compliance: Potential regulatory findings, audit issues, or contractual violations.
- Strategic: Delays to business goals, planned investments, or service expansion.
A product with limited monitoring capabilities may take more staff time to review alerts or investigate suspicious activity. The assessment should explain the effect on the MSSP’s operating model and identify what additional resources or integrations may be needed.
According to Qualysec, the NIST Cybersecurity Framework 2.0 provides “a structured, flexible, and comprehensive approach to managing and mitigating cybersecurity risks.” Its six functions offer a common structure for explaining how security gaps affect governance, protection, detection, response, and recovery.
How Can You Explain the Cost of Inaction?
Compare the estimated cost of addressing a gap with the potential cost of leaving it unresolved. The comparison should use documented estimates and clearly stated assumptions.
A business impact assessment may include:
- Estimated financial implications.
- Potential service disruptions.
- Existing risk exposure.
- Expected remediation expenses.
- Expected business outcomes.
For example, a hypothetical MSSP may estimate that improving access controls will require a $40,000 investment. If the current weakness also creates additional audit work, operational delays, or incident response expenses, management can compare those projected costs with the proposed investment.
Do not present estimates as confirmed losses. The figures need a source, a calculation method, or a clear explanation of the assumptions behind them. That gives management a fair basis for weighing the options.
How Should You Present Evidence to Support Gap Analysis Findings?
Every major finding should have traceable evidence, measurable indicators, and a clear comparison against the requirement. Management needs to know how the assessment reached its conclusions before approving a purchase, rejecting a product, or funding corrective work.
For product selection and audits, we link each finding to the requirement being tested and the evidence collected. A feature listed in a vendor’s documentation is not, by itself, proof that the product meets an MSSP’s operational needs. The assessment should show what was reviewed and what the evidence supports.
What Evidence Should You Include?
Six useful evidence sources are:
- KPI performance data.
- Audit and assessment results.
- Product and process documentation.
- Benchmark comparisons.
- Stakeholder interviews.
- Compliance assessment records.
For example, a finding about inadequate security monitoring may refer to monitoring records, system configurations, incident logs, or documented control requirements. If the issue concerns a product’s reporting capabilities, include the relevant test results or product documentation.
Which Visuals Make Findings Easier to Understand?
Choose a visual based on the question management needs to answer.
- Bar charts: Compare current performance with target KPIs.
- Heat maps: Show gap severity across products, departments, or assessment categories.
- Trend lines: Track changes in performance over time.
- Dashboards: Display remediation progress and unresolved findings.
- Comparison tables: Show product capabilities against requirements or benchmark results.
A product assessment dashboard, for instance, might show the number of critical findings, the percentage of requirements met, overdue remediation actions, and unresolved high-risk issues.
A chart should make a finding easier to understand. It does not need to appear on every slide. Include the assessment date, measurement criteria, and data source so management can judge whether the information is current and relevant.
How Do You Turn Gap Analysis Findings Into Actionable Recommendations?
Every recommendation should identify the gap it addresses, the expected result, the person responsible, and the deadline. A list of product deficiencies does not tell management whether to configure the existing solution, request a vendor change, introduce another tool, or choose a different product.
Recommendations should give decision-makers a clear course of action. They should also explain how the MSSP will check whether the action has resolved the problem.
What Should Every Recommendation Include?
Use seven components when documenting corrective actions:
- Identified gap.
- Proposed corrective action.
- Expected outcome.
- Required resources.
- Responsible stakeholder.
- Completion deadline.
- Success measurement.
For example, an assessment may find that a product does not support the access review process the MSSP requires. A recommendation could involve checking whether an available integration can provide the missing records, reviewing the limits of that approach, or evaluating another product.
The expected result needs a clear measure. “Improve access management” is too broad. A more useful target would specify that quarterly reviews must be completed for all designated systems, with approval records available for audit.
How Can You Distinguish Quick Wins From Long-Term Initiatives?
Some gaps can be addressed through configuration or documentation changes. Others may require additional investment, staff training, integration work, or a product replacement. Separate these actions so management can see the likely effort and timing.
| Initiative | Purpose | Planning approach |
| Quick wins | Address immediate deficiencies | Short-term actions |
| Medium-term improvements | Strengthen existing capabilities | Phased implementation |
| Long-term initiatives | Meet broader organizational requirements | Strategic roadmap |
At MSSP Security, we link proposed improvements to the original assessment findings. This gives management a way to check whether a recommendation addresses the problem identified during the product review.
Avoid promising results that the assessment cannot support. Recommendations should account for available resources, service requirements, and the limits of the product under review.
What Should a Gap Analysis Remediation Roadmap Include?
A remediation roadmap sets out the phases, milestones, resources, and owners involved in closing identified gaps. It turns approved recommendations into work that teams can schedule and track. When developing remediation plan gaps, teams should connect each identified deficiency to a corrective action, assign clear responsibilities, and establish realistic deadlines. For an MSSP introducing a new product, the roadmap may cover configuration, integration, staff training, testing, documentation, and operational handover. The exact activities depend on the product and the findings. Management should be able to see what needs to happen before the product is ready for use.
How Should You Organize Remediation Phases?
A four-phase structure can help teams plan the work:
- Phase 1: Address critical gaps. Deal with deficiencies that create immediate security, financial, compliance, or operational exposure.
- Phase 2: Implement high-priority improvements. Resolve significant weaknesses that need coordinated action.
- Phase 3: Strengthen processes and capabilities. Update documentation, training, technology, and internal controls.
- Phase 4: Validate results and monitor progress. Check whether corrective actions have met their stated requirements.
For cybersecurity work, the NIST framework can help group activities across governance, protection, detection, response, and recovery. These functions offer a reference for coordinating work across security responsibilities.
How Should You Present Ownership and Resource Requirements?
Management needs to know who will carry out each task and who is accountable for the result. A RACI matrix can make those roles clear.
| Role | Responsibility |
| Responsible | Executes remediation tasks |
| Accountable | Owns the final outcome |
| Consulted | Provides relevant expertise |
| Informed | Receives progress updates |
The roadmap should also identify budget needs, staffing requirements, and dependencies. Introducing a new monitoring process, for example, may call for technical resources, employee training, and management approval. Those requirements should be visible before implementation begins.
Set deadlines that reflect the work involved. Each milestone needs an owner and a clear completion condition. A schedule that ignores resource limits will be difficult to follow.
How Can You Secure Management Approval for Gap Remediation?
Management is more likely to make a clear decision when the presentation sets out the available options, their costs, and the consequences of each choice. A recommendation without a budget, owner, or expected result may leave executives unsure what they are being asked to approve.
End the briefing with specific requests. If the assessment concerns a new product, management may need to approve further testing, negotiate a vendor requirement, fund an integration, or reject the product.
Which Decisions Should Management Make?
Prepare the five decision areas relevant to the assessment:
- Which gaps need immediate attention?
- What remediation budget is available?
- Who owns each corrective action?
- Which initiatives should receive priority?
- What implementation timeline is acceptable?
For example, a critical security finding may require management to approve additional resources for access control improvements. The presenter should explain why the work is needed, what the organization expects to achieve, and what risks remain if the decision is delayed.
How Should You Present Different Options?
If more than one remediation approach is available, compare the options using the same criteria:
- Expected business impact.
- Financial requirements.
- Implementation complexity.
- Risk reduction.
- Resource availability.
A decision table can help management weigh the alternatives.
| Option | Main consideration | Management implication |
| Immediate remediation | Addresses urgent exposure | Requires faster resource allocation |
| Phased remediation | Spreads implementation effort | Requires milestone oversight |
| Deferred remediation | Delays corrective action | Requires acceptance of remaining risk |
Deferred remediation should involve documented risk acceptance by the appropriate authority. It should not become an informal way to leave serious deficiencies unresolved.
At MSSP Security, we keep product and remediation recommendations tied to the requirements identified during the review. Management can then consider the practical implications before approving a purchase, an implementation plan, or further vendor evaluation.
How Should You Track Progress After Presenting Gap Analysis Findings?
Track remediation through measurable indicators, milestone reviews, and regular reports. Management approval does not close a gap. The team still needs to complete the agreed work and verify that the original requirement has been met.
For MSSPs, this can include checking whether a selected product performs as expected after configuration and integration. A completed task is not necessarily proof that the product now meets the requirement. The result needs to be tested.
Which Metrics Should Management Monitor?
Six useful indicators are:
- Percentage of critical gaps closed.
- Remediation completion rate.
- KPI improvement.
- Outstanding high-risk findings.
- Budget utilization.
- Milestone completion.
A remediation dashboard might show that 75% of planned corrective actions are complete while several high-priority findings remain open. The completion rate alone does not explain the remaining exposure. Management also needs to know which issues are unresolved, why work is delayed, and whether any risk needs escalation.
How Often Should Management Receive Progress Updates?
Set the reporting schedule according to risk severity, implementation complexity, and management requirements. Progress reports may include:
- Remediation dashboards.
- Milestone tracking.
- Outstanding issue registers.
- Escalation procedures.
- Updated risk assessments.
The GAO Green Book lists monitoring as one of its five internal control components. It offers a reference for organizations reviewing control performance and following up on identified deficiencies.
Critical security findings may need more frequent reporting than routine improvements. Whatever schedule the team chooses, keep management informed between the original assessment and final validation.
When a gap is marked as closed, retain evidence that supports the decision. This may include test results, updated documentation, configuration records, or other material relevant to the original requirement.
How Should You Handle Management Questions and Feedback?
Answer management questions with assessment evidence, explain the limits of the review, and bring the discussion back to business requirements. Executives may challenge a severity rating, question the proposed budget, or ask whether a product can meet a requirement through another configuration.
These discussions can affect the final decision. Prepare for them before presenting the findings.
What Questions Might Senior Leadership Ask?
Be ready to answer six common questions:
- Why was this gap classified as critical?
- What evidence supports the finding?
- What happens if remediation is delayed?
- How much will corrective action cost?
- Can existing resources address the problem?
- How will the team measure success?
If management questions a critical security rating, explain the criteria used and show the supporting evidence. For a product review, identify the requirement the product failed to meet and explain how that shortcoming affects the MSSP’s services or operations.
How Should You Respond to Management Concerns?
Use a consistent approach when answering questions or resolving disagreements:
- Refer to the relevant assessment evidence.
- Explain assumptions and limitations.
- Present alternative solutions where appropriate.
- Clarify resource and timeline implications.
- Record decisions and follow-up actions.
Some questions will require further investigation. If the available evidence is not enough, say what remains to be checked and agree on when the team will provide an answer. An unsupported response can create problems later, particularly when management is deciding whether to approve a product or accept a security risk.
Product assessments can involve several departments, technical dependencies, and vendor requirements. At MSSP Security, we treat communication as part of the review process, not something that ends when the presentation is over. Documented decisions and follow-up discussions help keep the next steps tied to management’s requirements.
FAQ
What Is the Best Way to Present Gap Analysis Findings to Management?
The best approach is to summarize the key findings, compare current performance with target requirements, and explain the business impact of each gap. Prioritize issues based on risk and supporting evidence, then provide actionable recommendations with clear owners, deadlines, and required management decisions.
What Should an Executive Summary for a Gap Analysis Include?
An executive summary should include the assessment purpose, scope, overall results, critical findings, business implications, and recommended actions. It should give executives enough context to understand the main deficiencies and determine which actions require approval.
How Do You Prioritize Gap Analysis Findings?
Prioritize findings based on severity, business impact, risk exposure, urgency, and remediation effort. Critical gaps that threaten security, compliance, or service delivery should receive immediate attention, while less urgent deficiencies can be addressed through planned improvements.
What Evidence Should Support Gap Analysis Findings?
Supporting evidence may include KPI data, audit results, product documentation, benchmark comparisons, stakeholder interviews, and compliance assessment records. Each finding should connect the evidence to a specific requirement so management can understand how the assessment reached its conclusions.
How Do You Turn Gap Analysis Findings Into an Actionable Remediation Plan?
Translate each finding into a corrective action with a defined objective, responsible stakeholder, required resources, completion deadline, and success measurement. Organize actions by priority, establish implementation milestones, and monitor progress through regular management reports.
How Can Gap Analysis Findings Be Turned Into Management Decisions?
A successful gap analysis presentation helps management understand product deficiencies, business risks, and the actions needed to address them. MSSP Security provides vendor-neutral consulting to help MSSPs evaluate security products, reduce tool sprawl, optimize technology stacks, and improve service quality.
With over 15 years of experience and 48,000+ projects completed, our services include needs analysis, vendor shortlisting, PoC support, and actionable recommendations. Contact MSSP Security to build a technology stack aligned with your business goals and operational maturity.
References
- Mohamed, Abdalla. “Human Error Cybersecurity Statistics 2026: 35+ Facts.” DeepStrike, October 4, 2026. Updated October 22, 2026. Accessed November 4, 2026.
- Sahoo, Chandan. “NIST Cybersecurity Framework 2.0: Everything CISOs and Tech Leads Need to Know.” Qualysec, October 6, 2026. Accessed November 4, 2026.